You drive innovation. We manage security. Together, we accelerate compliance.
Navigating compliance frameworks, such as FedRAMP, DoW IL4 or IL5, GovRAMP, and HITRUST, isn’t just difficult — it’s resource-intensive, time-consuming, and easy to get wrong. Project Hosts simplifies the journey. We provide fully managed cloud compliance services that reduce your lift, accelerate certification, and keep you secure long after you’re listed.
No matter your needs, we’re here to help. With 20+ years of experience, we’ve seen the most common roadblocks and built a model to help you overcome them.
You want to grow your public sector footprint, but compliance is slowing you down.
You need certification quickly, without getting buried in documents or delays.
Your internal team lacks the time and expertise to manage an ATO or continuous monitoring.
Traditional compliance paths are expensive, financially unpredictable, and full of hidden variables and scope creep, making accurate budgeting and planning nearly impossible.
Getting certified is just the start. You need to build a secure environment and ensure you stay compliant.
You need help identifying, engaging, and securing the right sponsor or Mission Partner to move your initiative forward.
Project Hosts delivers turnkey compliance through a proven process to remove complexity from your hands and places it in ours. Here’s what that looks like:
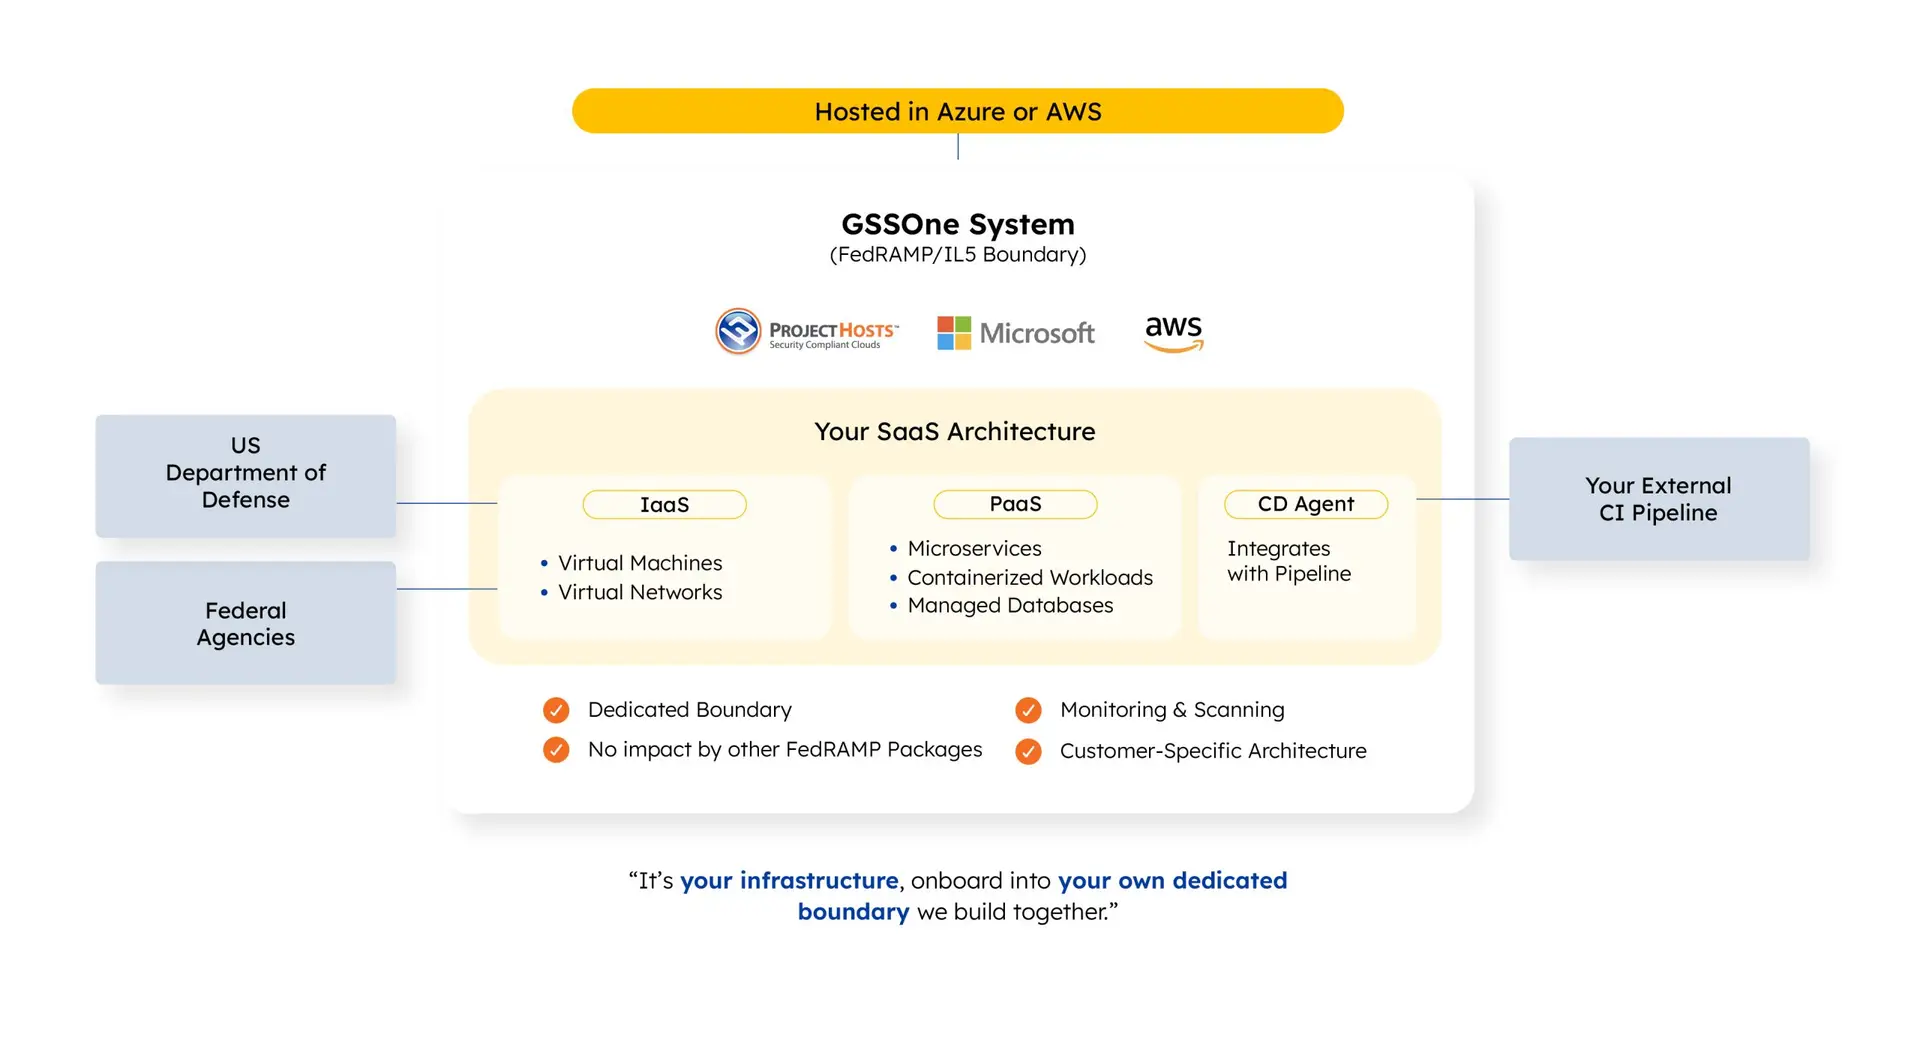
Inherit up to 75% of required controls through our FedRAMP, DoW, and HITRUST-certified GSSOne solution, built on Azure and AWS.
Focus on your core business while we write your SSP, collect evidence, and fully manage audit coordination, preparation and documentation.
Stay on a fast track with a dedicated Customer Success Lead and direct access to our compliance and engineering teams.
Maintain continuous compliance after certification with ongoing monitoring, patching, scanning, and incident response — fully managed by us.
Choose the path that fits your business case with flexible pacing, modular support, and the ability to transition operations in-house when ready.
Whether you’re pursuing FedRAMP, DoW, GovRAMP, or HITRUST, we use a consistent, proven process to drive results:
1
We build your dedicated testing and production environments on our secure GSSOne solution.
Your application inherits up to 75% of the required controls from our pre-certified environment.
Our team conducts a live gap analysis and architecture review.
2
We write your SSP, gather artifacts, and compile supporting evidence.
An internal QA review identifies and resolves issues before assessment.
You focus on your product — we handle the rest.
3
We coordinate directly with your third-party assessor (3PAO) and agency sponsor, if applicable.
Our team leads the audit process, represents your interests, and manages remediation.
Once approved, we help finalize your certification package for Marketplace submission.
The Project Hosts GSSOne compliance platform delivers an open architecture, providing the flexibility to design and build your software without constraints or disruption.
Our standards-based architecture is modular by design to support the easy integration of new features, services, and third-party tools.
It’s interoperable across vendors and ecosystems, enabling you to plug in your own services or tools with minimal friction and less proprietary “lock-in.”
You can take compliance in-house, if you prefer, with our structured transition program.
20+ years of regulated cloud experience.
Trusted by more than 35 U.S. government agencies.
Project Hosts does the heavy lifting. We implement and fully manage compliance, including creating policies and procedures, writing your SSP, handling all documentation, evidence collection, audit prep, representation, and continuous monitoring.
You get your own Marketplace listing — never shared under a common boundary.
Full coordination and guidance of ATO process, including representation and support with Agencies, Mission Partners, the FedRAMP PMO, DISA, and 3PAOs.
You reduce risk and burden without sacrificing speed, visibility, or control.
You proactively stay compliant with full monitoring, patching, and support from our experts.
Our HITRUST-certified environment also supports HIPAA compliance, making it easier for healthcare and software providers to migrate into the cloud with confidence.
From system documentation to evidence collection, assessment prep to continuous compliance, our team handles the heavy lifting so yours can stay focused on core priorities.
Go live in months, not years, with a pre-audited foundation that minimizes your audit scope.
With over 20 years of helping ISVs and healthcare providers navigate regulated cloud environments, we know how to simplify the complex and deliver results that hold up under scrutiny.
GSSOne is designed for interoperability. Our open architecture supports the easy integration of third-party tools, services, and components without vendor lock-in or disruption.
Whether you build on Azure or AWS, we give you the freedom to design your stack your way. GSSOne doesn’t limit your toolset — it supports it.
Our engineers monitor, patch, and protect your environment to ensure you remain HITRUST-compliant not just at audit time, but all the time.
Once you’re certified, we offer a structured transition program so you can take full control of your environment whenever you’re ready. Most clients choose to keep compliance off their plate — but if you want to bring it in-house, we make that easy.
Lay the foundation for success while we help you build your business case, understand the compliance process, and spark agency interest.
Take the next step toward certification. With our guidance, you can reach key milestones while moving at the pace of your initiative.
Allow us to help finalize documentation, implement controls, and prepare you for a successful audit. After certification, we’ll provide continuous monitoring, scanning, and more.
Reach out and tell us more about how we can ease the burden of cloud security compliance.